TLS Certificates in the HomeLab with Hurricane Electric, Let's Encrypt, OpenWRT and TrueNAS
I finally sat down to get proper TLS certificates for my homelab set up. What I wanted was to use the domain I have already set up at Hurricane Electric for DDNS, also for my home network and TLS certificates. I decided to have OpenWRT do the ACME work and then distribute the the certificates to the servers that need it. More on the „how” later on.
Hurricane Electric as the DNS provider, because they provide an API for DNS-01 challenge while my domain-dealer and nameservice provider still does not provide an API for DNS changes. :/ So while I already had „homeip.example.com¹” already set up for DDNS, I decided to use „lan.example.com¹” for my home network an dus a wildcard certificate for the individual servers/services inside that network.
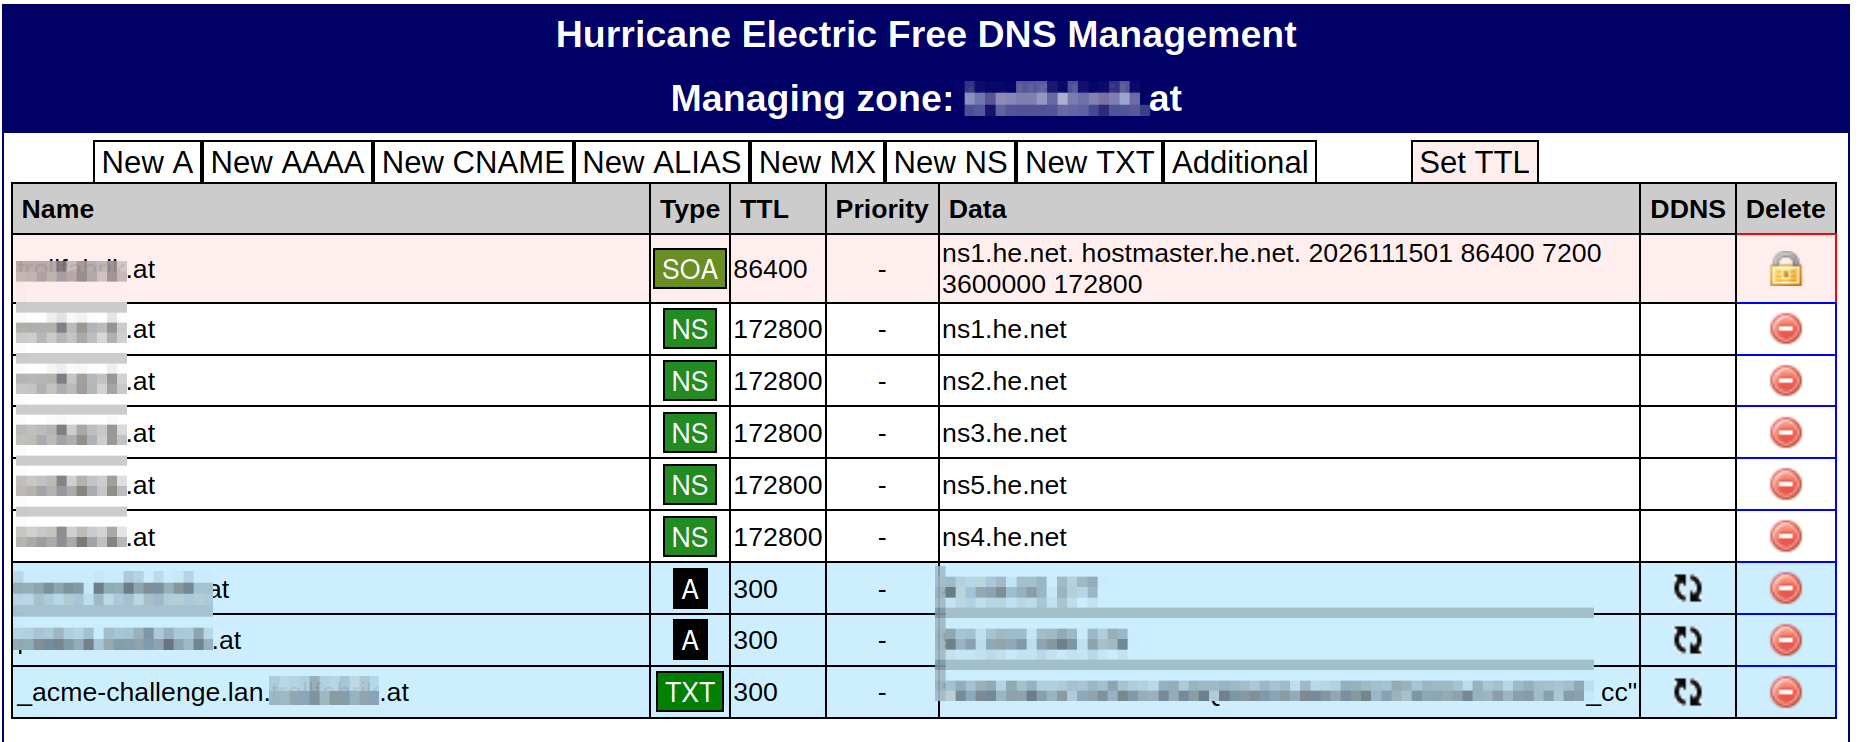
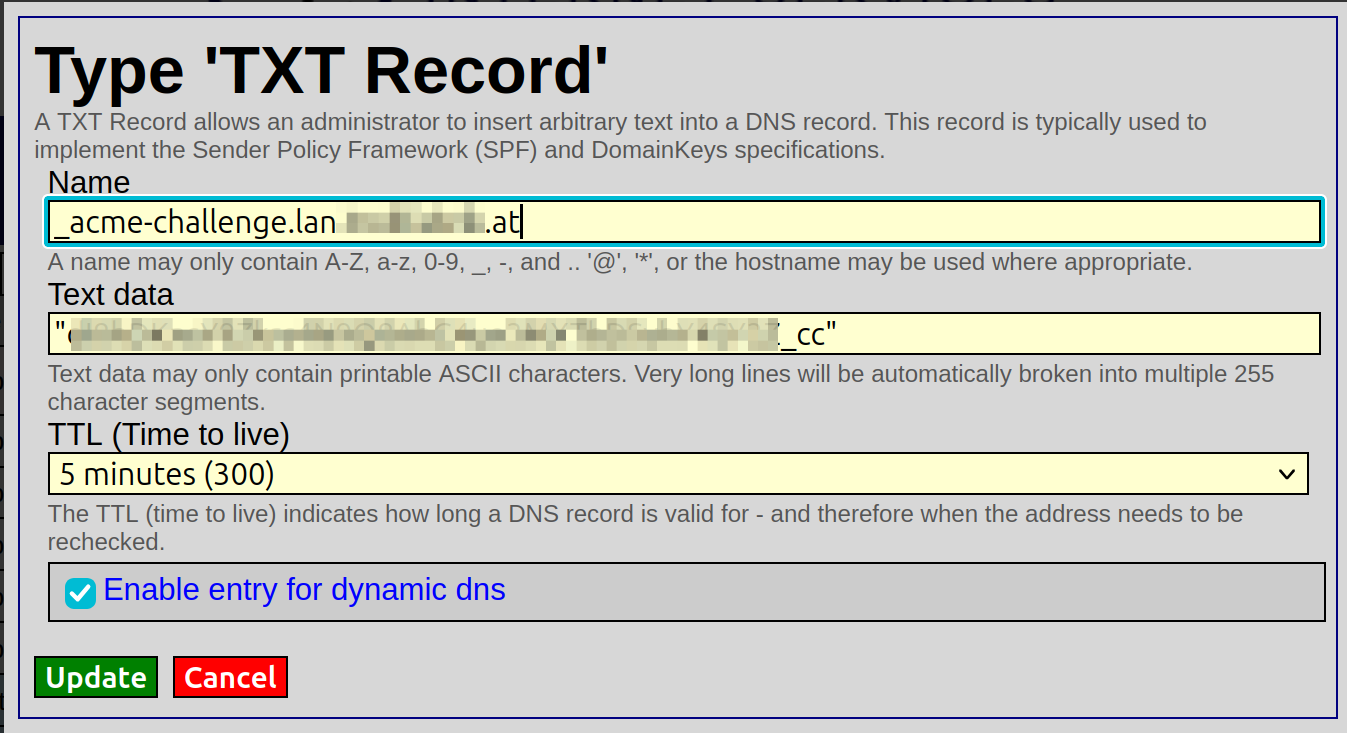
The initial setup at Hurricane Electric (HE) was quite easy, You do need to set up the TXT DNS record for ACME DNS-01 challange manually once, as the API does not support creatio or deletion, which is fine for me. So after a little bit of non-LLM supported reading, I found the correct notation for a wildcard ACME challenge entry („_acme-challenge.lan.example.com”, yes, the leading underscore is important. Ask me, how I know) and added that to the DNS entry:
The important part with the TXT record is to not forget the leading underscore in the name and to set the TTL to 5 minmuntes. Additionally, do not forget to set the checkbox „Enable entry for dynamic dns”.
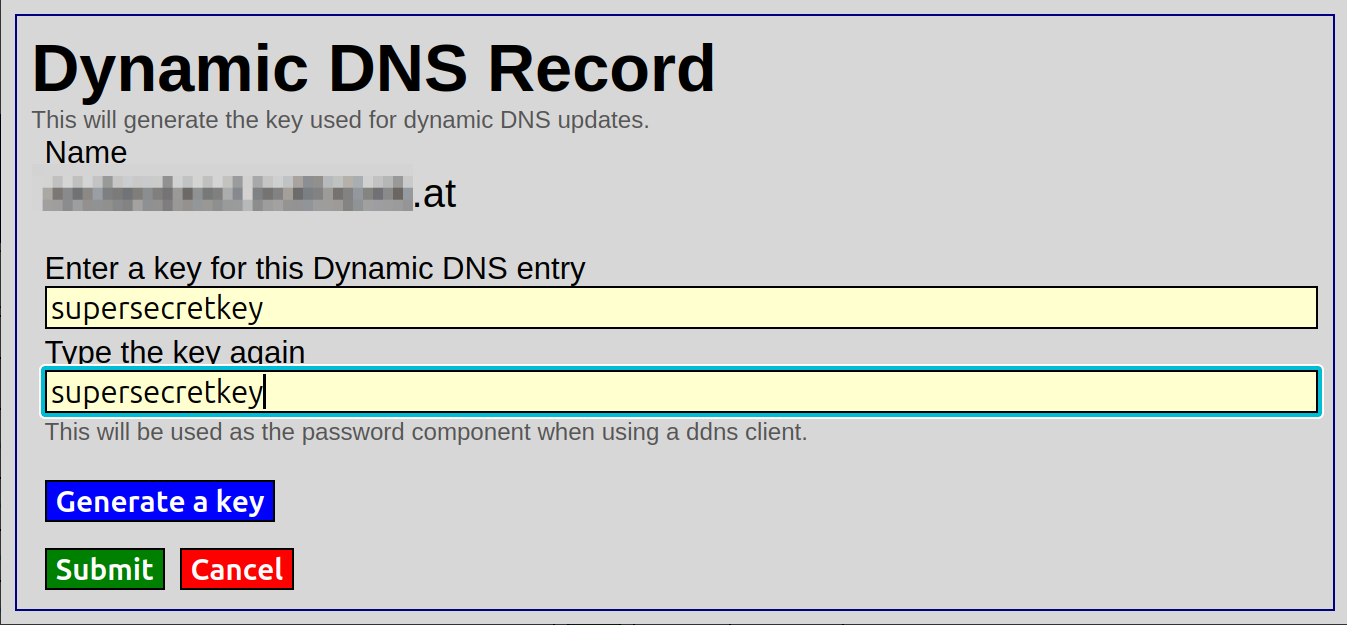
This allows you to set a key that you can later use in OpenWRT to authenticate to the HE API.
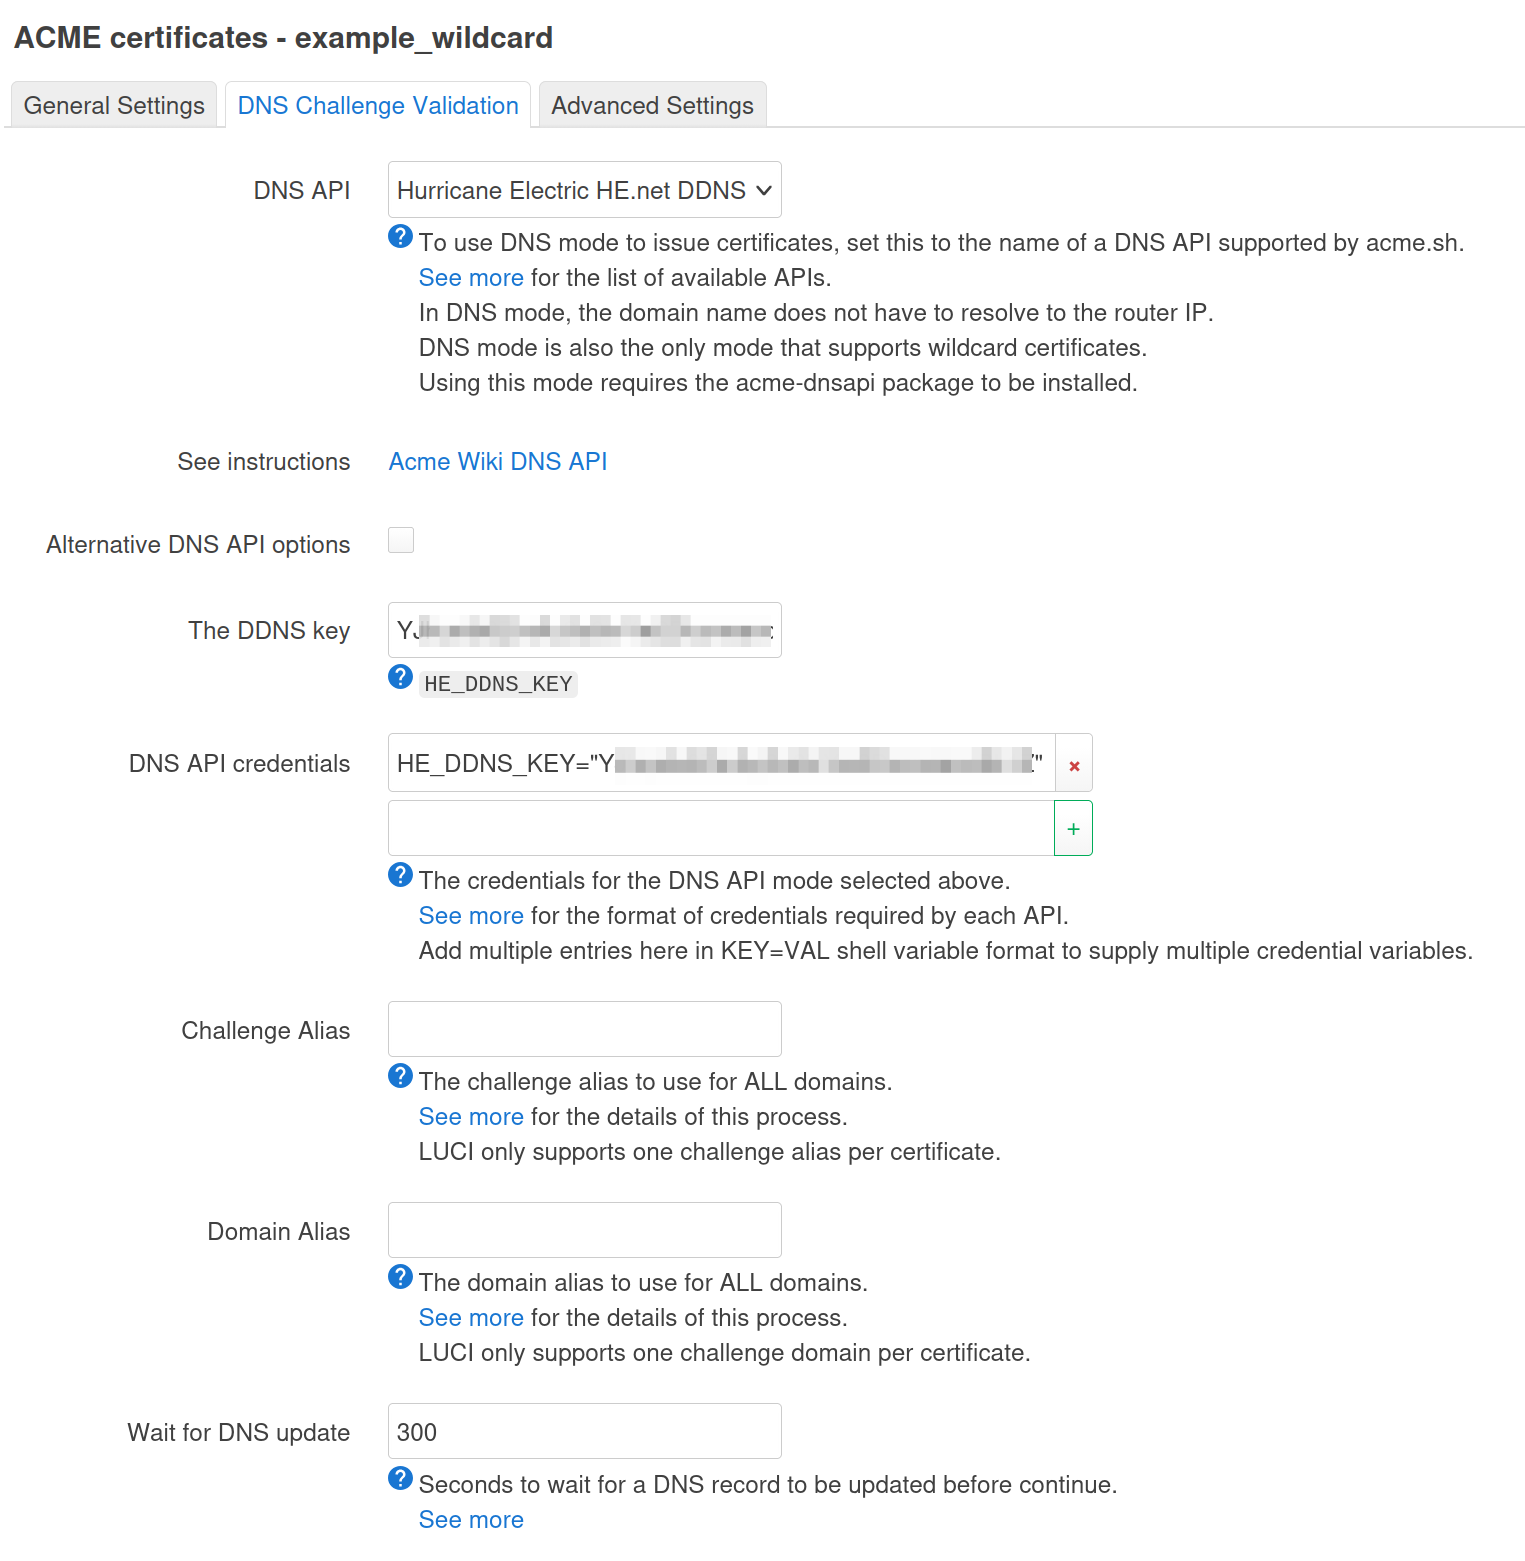
Next step was set up OpenWRT to interact with Let’s Encrypt and Hurricane Electric to get the TLS certificates. Ther eis good documentation available at „Get a free HTTPS certificate from LetsEncrypt for OpenWrt with ACME.sh” for the general setup (which is basically „apk add luci-app-acme” on the command line or via LuCI).
The only thing that tripped me was the „DNS Challange Validation” tab of the ACME configuration form in OpenWRT. When you select „Hurricane Electric HE.net DDNS” as the „DNS API”, the UI will provide you with a prompt for the DDNS key you just created earlier on the HE site and it will create the „DNS API credentials” entry with it. You can delete the other entries there. The mistate I did was to enter domains in „Challange Alias” and „Domain Alias” which confused the heck out of the syste. Once I removed those, everything worked like a charm. The only other thing is to set the „Wait for DNS update” to 300 seconds, as HE might need up to 5 minutes to update the DNS entry after you modified it via the API.
I would suggest to configure it towards the Let’s Encrypt staging server first to iron out any kinks, before you switch to their production servers. OpenWRT’s ACME UI offers you an option for that in the „Advanced Settings”.
Once this is properly set up and I waited the obligatory 5 minutes, I had my Let’s Encyrpt certificates stored in /etc/acme/lan.example.com_ecc ready to use.
So a quick edit to /etc/config/uhttpd:
config uhttpd 'main'
	list listen_http '192.168.1.1:80'
	list listen_https '192.168.1.1:443'
	…
	option cert '/etc/acme/lan.example.com_ecc/fullchain.cer'
	option key '/etc/acme/lan.example.com_ecc/lan.example.com.key'
	…
followed by a service uhttpd reload and my OpenWRT box was using the Let’s Encrypt certificate.
But how to get that certificate to my TrueNAS box. Of course I could set up the whole ACME stuff there as well, but there has to be a better way. And there is. Again, without the help of an LLM, I found „deploy-truenas”, a Python script to deploy TLS certificates to a TrueNAS SCALE/Community Edition server using the TrueNAS Websocket API.
A quick apk add python3 python3-openssl python3-requests installed the prerequisites and once I had an API key generated on TrueNAS, all I had to do was copy over the „deploy_config_truenas.example” file to „deploy_config_truenas” and modify the necessary values (TrueNAS server IP, API Key and location of the cerificates to copy).
I gave this a whirl manually /usr/deploy-freenas-master/deploy_freenas.py --config /usr/deploy-freenas-master/deploy_config_truenas
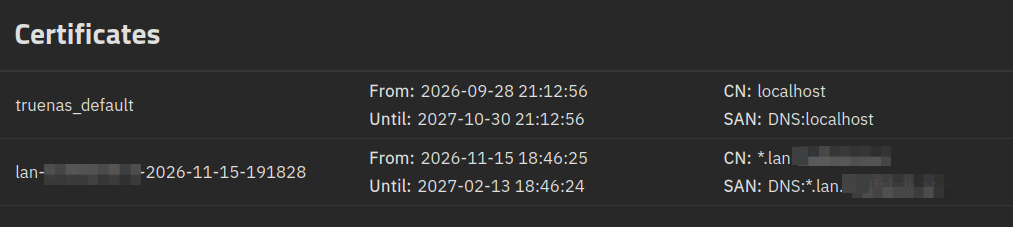
and lo and behold, TrueNAS switched to the Let’s Encrypt certificate and lists it in the GUI:
So all I had to do now was to create /etc/hotplug.d/acme/00-truenas with the content
if [ "$ACTION" = "renewed" ]; then
	/usr/deploy-freenas-master/deploy_freenas.py --config /usr/deploy-freenas-master/deploy_config_truenas
fi
so that the certificate on the TrueNAS box gets updated with every certificate renew.
Rather easy, if you know what you are doing. A few hours, if you have to read up on everything and add some trial-and-error to it.
¹ … Names have been changed to protect the innocent.
Tagged as: he, homelab, hurricane, openwrt, security, tls, truenas | Author: Martin Leyrer
[Sonntag, 20261115, 19:30 | permanent link | 0 Kommentar(e)